Account Security Overview
Your Serene Creations account is the single point of access to your tenant configuration, subscriber data, contact messages, and billing settings. This article walks through the three baseline security steps every account holder should complete before going live.
Before you begin
You will need:
- An active Serene Creations account (the one created during sign-up).
- An authenticator app installed on a mobile device — Google Authenticator, Authy, 1Password, or any TOTP-compatible app works.
If you have not yet created your account, start with Tenant Setup first.
Step 1: Enable multi-factor authentication
MFA adds a second verification step at every sign-in. After entering your password you are prompted for a time-based one-time code (TOTP) generated by your authenticator app. Even if your password is compromised, an attacker cannot sign in without the physical device that holds your MFA secret.
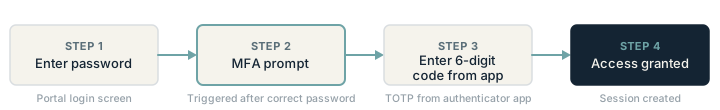
To enable MFA:
- Open the admin portal and navigate to Account → Security.
- Select Enable authenticator app.
- A QR code appears. Open your authenticator app, choose Add account (or the
+icon), and scan the code. - Your app displays a six-digit code that rotates every 30 seconds. Enter the current code into the portal to confirm the pairing.
- The portal shows a set of one-time backup codes. Copy these and store them somewhere safe — a password manager works well. Each backup code can be used once to regain access if you lose your device.
- Select Confirm and activate.
Once MFA is active, each sign-in requires both your password and a fresh code. If you see “Invalid code,” wait for the code to rotate and try again — the codes are time-sensitive and your device clock must be accurate.
If you lose your authenticator device, use one of your backup codes to sign in, then immediately re-enroll with a new device under Account → Security → Remove authenticator app followed by Enable authenticator app.
Step 2: Review your session policy
Sessions expire after 24 hours of inactivity by default. This is the recommended setting for most workflows — a day of normal use without re-authentication, but automatic sign-out if you step away overnight.
To adjust the timeout:
- Go to Account → Security → Session timeout.
- Choose a shorter window if your environment is shared or you prefer more aggressive lock-out.
- Save. The new timeout applies to new sessions; existing sessions keep the old timeout until they expire.
Step 3: Audit active sessions
Every active sign-in is listed under Account → Security → Active sessions. Each row shows:
| Column | What it means |
|---|---|
| Device | Browser and operating system inferred from the user-agent |
| Location | Approximate city from IP geolocation (may be a CDN edge location) |
| Last active | Timestamp with 24-hour clock and UTC offset |
| Current | Marked on the session you are using right now |
If you see a session you do not recognise, select Revoke immediately. Revoking a session signs that device out and invalidates its token. If you suspect account compromise, revoke all sessions, change your passphrase, and re-enroll MFA with a new backup code set.
Passphrase recommendations
| Recommendation | Why |
|---|---|
| Minimum 16 characters | Length is the strongest defence against brute-force |
| Unique to this account | A reused password is only as strong as the weakest site it appears on |
| Use a password manager | Eliminates reuse and removes the burden of memorising long passphrases |
A random four-word passphrase (e.g. correct-horse-battery-staple) is easier to remember than a short random string and is significantly stronger. Your password manager’s generator works too.
Next steps
- MFA setup in detail — step-by-step with screenshots and backup-code recovery.
- Tenant Setup — configure your workspace after securing your account.